APSER MSP on AWS
Experience and Talent at your disposal for the secure management of your current platform on Amazon Web Services
The right service for your business
Outsourcing platform management to AWS enables organizations to optimize resources and costs by accessing the specialized expertise of third-party providers who are up to date with the latest technologies and best practices. This not only improves operational efficiency and system security, but also frees up the internal team to focus on strategic activities and innovation, rather than routine infrastructure management. In addition, outsourcing can offer scalability and flexibility, quickly adapting to changing business needs.
1. Accelerate
2. Reduce
3. Improve
Why outsource my platform management to apser
Outsourcing the AWS cloud platform to apser offers multiple key benefits. First, it allows businesses to leverage the partner’s advanced expertise and experience, which is continuously up-to-date with the latest technologies, best practices, and industry regulations. This ensures management is streamlined, secure, and compliant with the most demanding standards. Furthermore, apser provides proactive and personalized support, rapid scalability, and solutions tailored to specific business needs – all of which are difficult to replicate internally without incurring high costs and effort. By outsourcing, businesses also free up their internal teams to focus on strategic initiatives, innovation, and growth, rather than day-to-day operational tasks.

Do you know what level of support your infrastructure needs?
Hermes guides you on support, operation, and managed services in AWS.
Evaluate supportMain Features
These capabilities provide a comprehensive framework for effectively managing an AWS cloud platform, ensuring that resources are optimized, secure, and meet the operational and strategic needs of the business.
1. Identity and Access Management (IAM)
Access Control : Configure and manage permissions for users, groups, and roles using IAM (Identity and Access Management). Establish policies that determine who can access which resources and under what conditions.
Authentication and Authorization : Implement multi-factor authentication (MFA) measures and manage access keys and certificates to ensure user authenticity.
2. Resource Management
Instance Launch and Configuration : Deploy and manage EC2 instances, configuring their resources (CPU, RAM, storage) and ensuring they are properly sized for workloads.
Storage : Manage EBS, S3, Glacier, and other storage services. Configure backups, replication, and disaster recovery.
Networking and Connectivity : Configure VPCs (Virtual Private Clouds), subnets, routing tables, gateways, and NATs. Manage secure connectivity between cloud services and on-premises networks.
3. Monitoring and Maintenance
Resource Monitoring : Use CloudWatch to monitor resource usage, performance, and receive alerts when operating parameters fall outside acceptable ranges.
Logging and Auditing : Implement CloudTrail to track all actions performed within the platform, enabling security and compliance audits.
Proactive Maintenance : Schedule updates, security patches, and automatic backups to ensure all infrastructure components are up-to-date and protected.
4. Security
Data Encryption : Configure encryption in transit and at rest for all sensitive data using services such as AWS KMS (Key Management Service).
Network Security : Configure security groups, access control lists (ACLs), and other firewall mechanisms to protect incoming and outgoing network traffic.
5. Cost Management
Cost Optimization : Use tools like AWS Cost Explorer and AWS Budgets to monitor and optimize spending, identify underutilized resources, and adjust capacity according to demand.
Tags and Categorization : Implement a tagging system to categorize resources and facilitate cost management and expense allocation.
6. High Availability and Disaster Recovery
Load Distribution : Configure load balancers (ELB), Auto Scaling Groups, and multi-zone configurations to ensure high availability of applications.
Disaster Recovery : Establish DR (Disaster Recovery) plans and configurations, including automatic backups and data replication across multiple regions.
7. Automation and Management of Infrastructure as Code
Deployment Automation : Use AWS CloudFormation, Terraform, or AWS CDK (Cloud Development Kit) to manage infrastructure as code, enabling reproducible and consistent deployments.
Task Automation : Implement scripts and Lambda functions to automate routine tasks and reduce manual intervention.
8. Compliance and Governance
Regulatory Compliance : Ensure that the infrastructure complies with regulations and standards such as GDPR, HIPAA, SOC 2, etc.
Governance Policies : Implement governance policies and practices to ensure the proper management of resources and data within the platform.
9. Support and Incident Resolution
Documentation and Support Procedures : Maintain clear and accessible documentation of infrastructure and troubleshooting procedures.
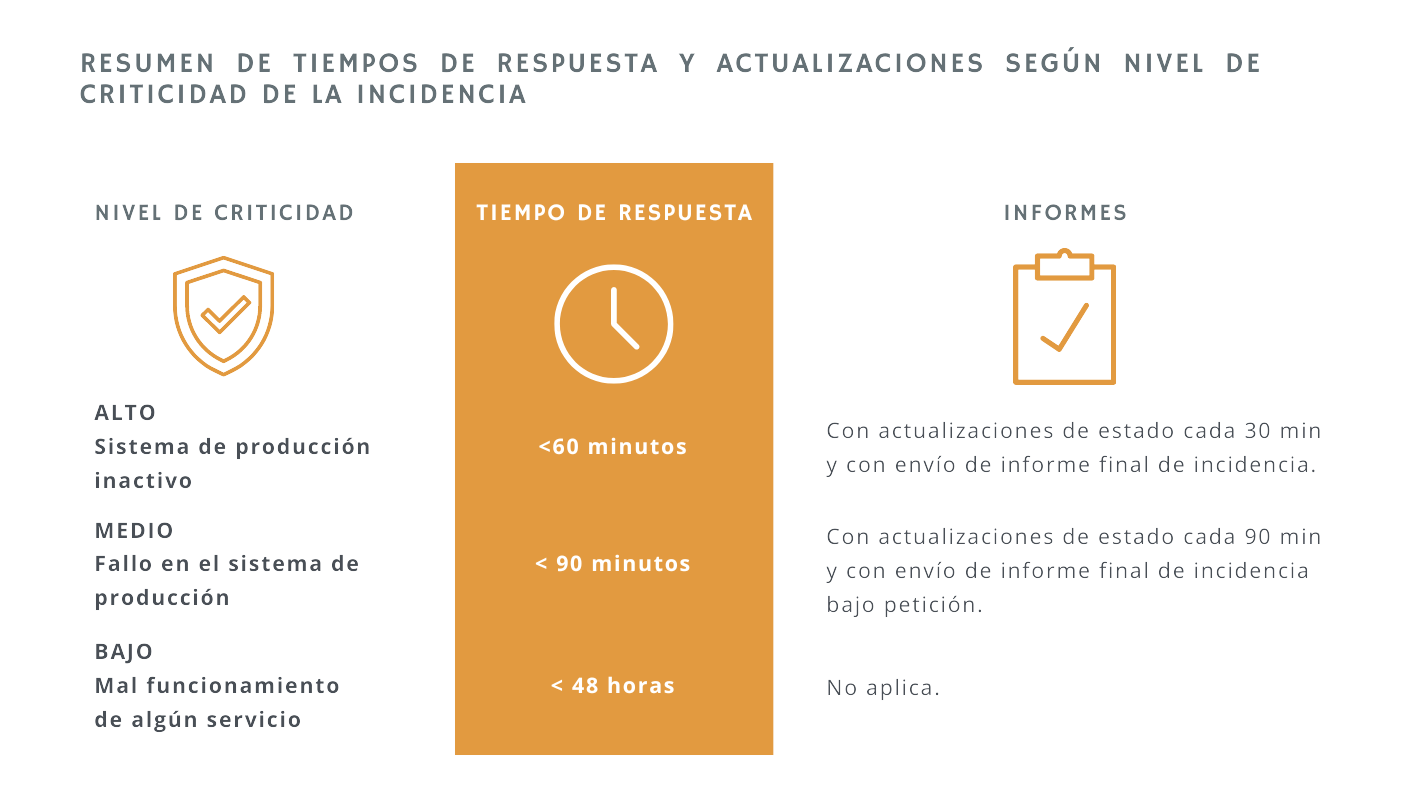
Incident Response : Establish an incident response plan, including the identification, mitigation, and resolution of critical problems.
Do you need more info?
Fill out the form and we will contact you to make a personalized MSP proposal to meet your needs.